One call, one email and the money is gone
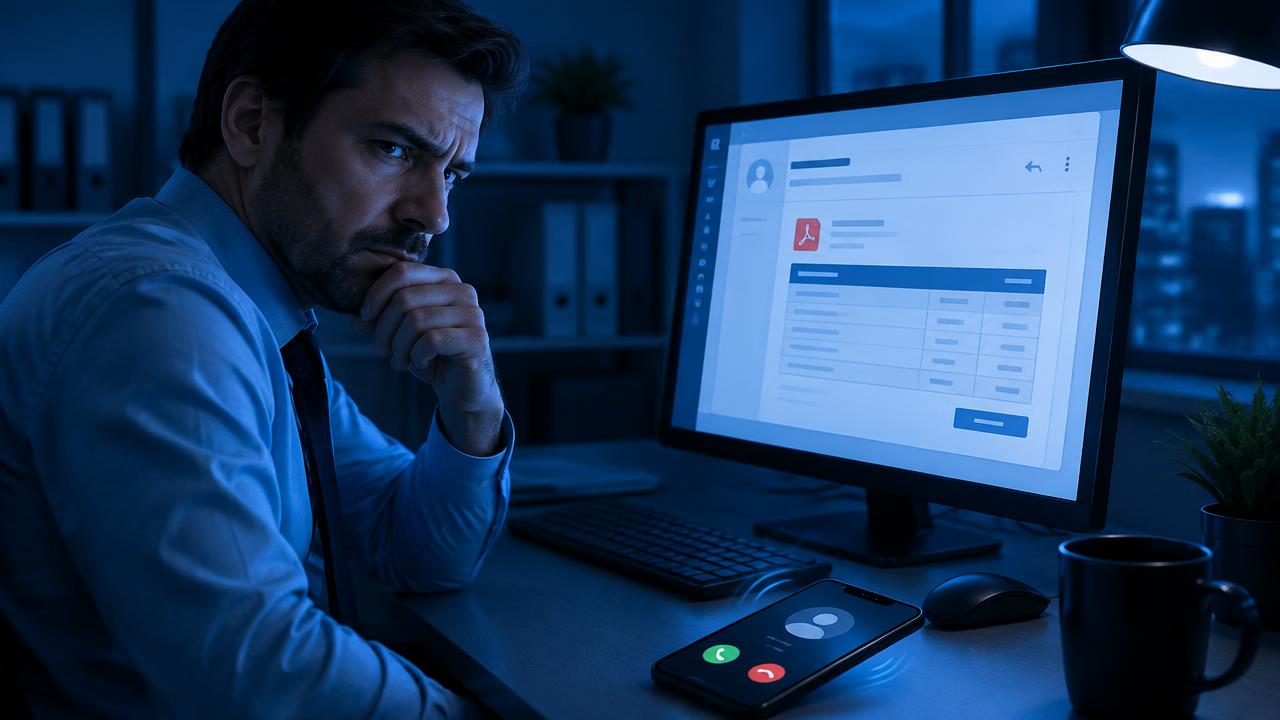
"Hi, this is the managing director. I'm in a confidential acquisition and need a transfer today." That's how CEO fraud often starts. A related scam is invoice fraud: a supposed supplier announces that their bank details have changed.
Neither trick needs malware. They exploit time pressure, authority and routine. And they hit small businesses hard, because one person often makes payments alone.
How fraudsters work
- Research: names, roles and suppliers are on the website, LinkedIn or in the commercial register.
- Build trust: the email comes from an almost identical domain, from a real supplier's hijacked mailbox, or is backed by a phone call.
- Apply pressure: "confidential", "today", "don't tell anyone".
- Redirect payment: to a new account, often abroad or at an online bank.
What's new is that voices can be imitated with AI. A call in your boss's familiar voice is no longer proof.
The key rule: call back on a known number
Every change of bank details and every unusual payment instruction is confirmed through a second, known channel. Not the number in the email, but the one from your records or an old contract.
More safeguards
Organisational
- Four-eyes principle for payments above a set amount and for new payees
- A written rule that management never requests secret urgent transfers by email
- Master data changes only after a call-back, noting who confirmed and when
- A code word for genuine emergencies that is never sent by email
Technical
- MFA on all mailboxes so your own account can't be abused (password managers and MFA)
- SPF, DKIM and DMARC for your domain (guide)
- An "External email" tag in the subject or a banner
- Warnings for look-alike sender domains if your mail system supports it
What to do if it happens
- Call the bank immediately and try to recall the payment. Every hour counts.
- File a police report, in Saxony-Anhalt for example via the police online service.
- Check the mailbox: was an account taken over? Change passwords, check forwarding rules.
- Notify your insurer if you have cyber insurance. Many policies treat deception fraud separately.
- Check data protection: if personal data leaked, a reporting duty may apply.
Common mistakes
- Changing bank details "quickly" because the email looked genuine
- Calling back the number in the suspicious email's signature
- Embarrassment: victims report too late
FAQ
Does training really help? Yes, especially with concrete examples from your own work. Anyone who has seen the scam once is more likely to spot it. See also recognising phishing.
Are we too small to be a target? No. Small businesses rarely have a four-eyes rule, which makes them attractive.
Conclusion
Clear processes are the best defence against CEO and invoice fraud: call-backs, four eyes and no exceptions under time pressure. To secure the technical basics, see our IT security services.